Listen to the article
AI agents could take on repetitive investigations, shifting security teams towards incident ownership, SOC engineering and exposure management , while keeping human oversight essential.
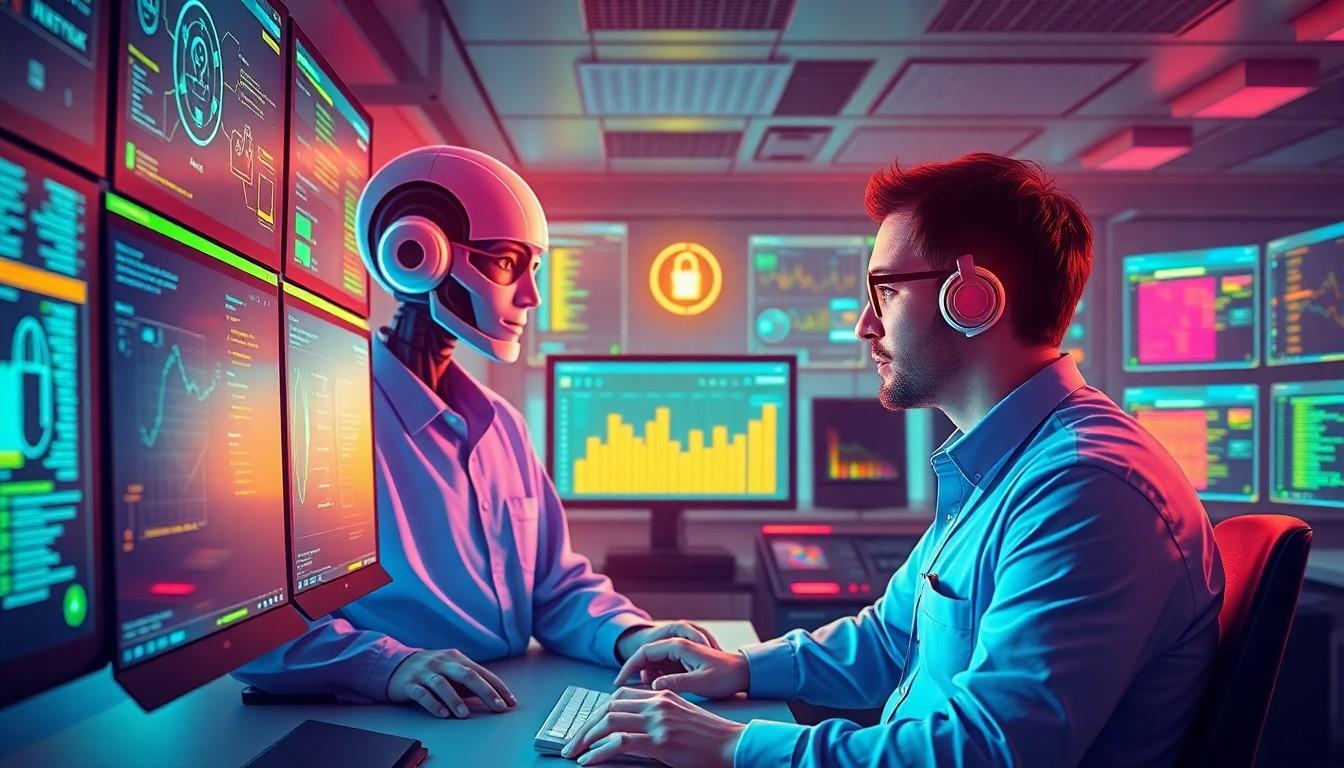
Artificial intelligence is beginning to reshape the security operations centre in ways that go well beyond faster alert handling. A sponsored summary of Gartner’s 2026 research suggests that AI agents are not simply helping analysts process more notifications, but are altering how security teams organise work, assign responsibility and judge performance. The broader implication is that repetitive investigation may increasingly be delegated to machines, while human specialists retain ownership of judgement-heavy tasks such as incident coordination, containment decisions and security engineering.
That shift matters because traditional SOCs have long been overwhelmed by the volume of alerts generated by endpoint tools, cloud systems, identity platforms and threat-intelligence feeds. Gartner’s public abstract, published in February 2026, warns that inefficient security operations can contribute to missed threats and slower incident response, and advises teams to evaluate AI SOC agents for detection, prioritisation and response while keeping expectations realistic. NVIDIA has made a similar case in a separate discussion of agentic AI, arguing that automated systems can gather context, correlate data and prepare structured reports, reducing the time analysts spend on repetitive triage tasks. The common theme is not the removal of humans, but the redistribution of effort.
One likely consequence is a move away from measuring analysts by alert counts alone. As AI systems take on more of the initial investigation work, the human role increasingly resembles case ownership: understanding the wider incident, assessing business impact, coordinating response across teams and ensuring that containment and remediation are completed properly. That would mark a meaningful change in operating culture. Instead of acting mainly as alert processors, analysts become responsible for driving an event to resolution, with the emphasis on outcome rather than throughput.
The same transformation also raises the profile of SOC engineering. Building and maintaining automated workflows will require people who understand both security operations and software design, including how to connect SIEM, EDR, XDR and SOAR platforms, how to configure agent permissions and how to validate that automated investigations are reliable. NIST has argued that agent identity management should be built around least privilege, deterministic access decisions, monitoring and tamper-evident records, while Microsoft’s cloud security guidance similarly stresses scoped identities, approval for critical actions and strong logging. In practice, that means organisations will need to treat AI agents as operational systems that must be engineered, tested and supervised, not as plug-and-play assistants.
Another area drawing renewed attention is exposure management. Rather than waiting for suspicious activity to appear, security teams are increasingly expected to identify where they are most vulnerable before an attacker takes advantage. CISA’s vulnerability-management guidance recommends prioritising remediation according to active exploitation, threat intelligence, severity and likely exploitability, rather than treating every flaw as equally urgent. In an AI-assisted SOC, that approach could be enhanced by correlating vulnerability data, asset inventories and live threat intelligence, especially where internet-facing systems or misconfigured cloud services are involved. Even so, any AI-generated risk ranking still needs human verification; a prioritised finding is not the same as proof of compromise.
The workforce and training implications are equally significant. Organisations may need fewer people dedicated purely to repetitive alert triage, but they are likely to need more specialists in detection engineering, threat hunting, exposure management, automation validation and incident response leadership. Microsoft’s incident-metrics guidance suggests that SOC performance should be judged using measures such as mean time to triage and mean time to resolve, rather than simple ticket volume. That logic fits the broader argument here: the real test of AI in security operations is not how many alerts it can close, but whether it improves response quality, reduces exposure and shortens the path to containment without creating new blind spots.
There are also new risks. An AI agent given access to security telemetry, credentials and response tools can itself become part of the attack surface if permissions are too broad, integrations are insecure or malicious input manipulates its behaviour. NIST and Microsoft both caution that prompt injection, privilege escalation and excessive access can undermine agent safety, while their guidance points towards logging, monitoring, approval gates and least-privilege design. The emerging model of the SOC therefore looks less like full automation and more like supervised autonomy: machines handle the repetitive work, but humans remain accountable for decisions, safeguards and the final security outcome.
Source Reference Map
Inspired by headline at: [1]
Sources by paragraph:
Source: Fuse Wire Services